
Securing your WordPress website is non-negotiable. But with hundreds of security plugins available, the process of choosing the right one can be daunting. Standard advice often just scratches the surface, recommending plugins without explaining the crucial differences between a Web Application Firewall (WAF), a malware scanner, or a login protection module. For instance, a WAF might block a SQL injection attack by filtering malicious GET requests, while a malware scanner detects a PHP backdoor file that was uploaded via a separate vulnerability. This leaves you guessing which features are truly essential for your specific setup.
This guide cuts through the noise. We provide an expert, in-depth analysis of the best WordPress security plugins available today, moving beyond generic feature lists. For each plugin, we dissect its core strengths, reveal potential limitations, and offer practical, real-world scenarios to help you make an informed decision. You’ll find detailed breakdowns, screenshots, and direct links to help you evaluate each option thoroughly.
Whether you’re a small business owner protecting customer data, an e-commerce retailer safeguarding transactions, or a marketing manager ensuring site uptime, this comprehensive resource is for you. We’ll examine leading solutions like Wordfence, Sucuri, SolidWP, and MalCare, comparing their performance impact, compatibility, and ideal use cases. Forget vague recommendations; this is your blueprint for building a resilient, multi-layered defense tailored to your website’s unique needs. We’ll help you select the precise tools needed to protect your most valuable digital asset from the ground up.
1. WordPress.org Plugin Directory
Before diving into individual tools, the essential starting point for finding the best WordPress security plugins is the official WordPress.org Plugin Directory itself. This isn’t a plugin but the authoritative repository where nearly every legitimate security tool begins its journey. Think of it as the foundational research platform for gauging a plugin’s reputation, stability, and community trust before you ever click “install.” It provides the raw data you need to make an informed decision, aggregating user reviews, active installation counts, and update histories in one place.
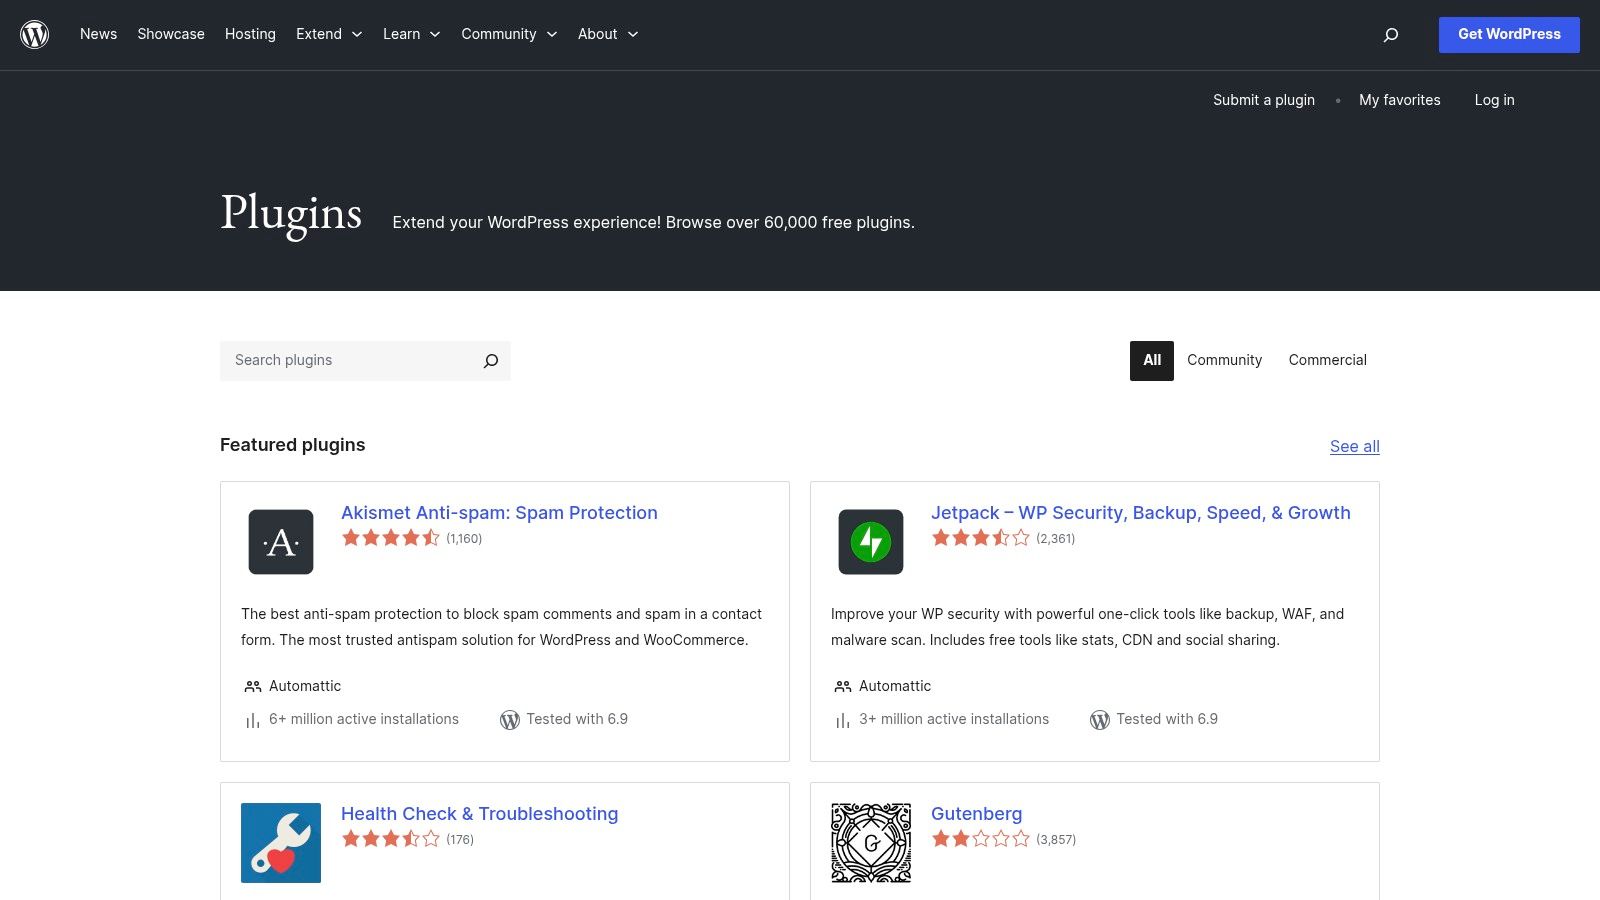
The platform is completely free to use and offers unparalleled transparency. For any given plugin, you can immediately see when it was last updated, a critical signal for security software. For example, if you see a plugin hasn’t been updated in over a year, it’s likely incompatible with modern PHP versions or vulnerable to new exploits. Conversely, an active changelog shows the developer is patching vulnerabilities and improving features, while high active install counts (e.g., over 1 million) and positive ratings signal widespread trust and reliability. The directory’s value lies in this unfiltered, community-driven data.
Navigating the Directory Effectively
To maximize its utility, don’t just look at the star rating. Dive into the “Reviews” tab and filter for one-star reviews to identify recurring issues. Check the “Support” forums to see how responsive the developers are to user problems. For example, seeing a developer resolve multiple user issues within 24 hours is a strong positive signal. Most importantly, review the “Advanced View” or “Changelog” to ensure the plugin is compatible with the latest version of WordPress and receives frequent security patches. This due diligence is the first line of defense.
| Key Feature | Why It Matters for Security |
|---|---|
| Last Updated Date | Shows if the developer is actively patching vulnerabilities. |
| Active Installations | Indicates widespread adoption and community trust. |
| User Reviews | Provides real-world feedback on performance and conflicts. |
| Support Forum Activity | Reveals developer responsiveness to user issues. |
- Pros: Official and trustworthy source, provides key quality indicators (updates, installs), completely free for research.
- Cons: Requires manual research to identify the best options, doesn’t offer direct security protection itself.
Website: https://wordpress.org/plugins/
2. Wordfence (Defiant Inc.)
As one of the most widely deployed endpoint security solutions, Wordfence is a go-to choice for website owners seeking a comprehensive, on-site defense system. It combines a Web Application Firewall (WAF) that runs on your server with a dedicated malware scanner, providing robust protection directly within your WordPress environment. This endpoint approach allows it to block malicious traffic before it hits your core files and identify threats that may already exist on your site, making it a foundational layer in your overall security posture.
The platform is backed by a mature threat intelligence team, which powers its real-time firewall rules and malware signature updates for premium users. This ensures the plugin is continuously adapting to new and emerging threats. Its free version offers a powerful baseline, while its tiered premium plans (Premium, Care, and Response) provide escalating levels of protection and hands-on support, catering to everyone from small bloggers to high-traffic e-commerce sites. Adhering to WordPress website security best practices is critical, and Wordfence provides the tools to implement many of them effectively.
Leveraging the Wordfence Firewall and Scanner
For maximum effectiveness, configure the firewall to run in “Learning Mode” for about a week after installation. This allows it to understand your site’s normal traffic patterns—like legitimate API requests from a mobile app—before you switch it to “Enabled and Protecting,” which prevents false positives. Schedule regular malware scans during low-traffic hours (e.g., 3 AM server time) to minimize any potential performance impact. For sites with multiple administrators, the Wordfence Central dashboard is an invaluable free tool for monitoring the security status of all your properties from a single interface.
| Key Feature | Why It Matters for Security |
|---|---|
| Endpoint Web Application Firewall (WAF) | Blocks malicious traffic at the server level before it reaches WordPress. |
| Malware Scanner | Scans core files, themes, and plugins for infections and backdoors. |
| Real-Time Threat Intelligence | Premium feature providing immediate updates for firewall rules and malware signatures. |
| Wordfence Central | Allows management of security for multiple WordPress sites from one dashboard. |
- Pros: Mature and widely trusted, offers a strong free version, multiple tiers (Free to Response) scale with security needs.
- Cons: Per-site licensing can become costly for agencies, can be resource-intensive on shared hosting if not configured carefully.
Website: https://www.wordfence.com/
3. Sucuri
Sucuri shifts the security paradigm from on-site scanning to cloud-based edge protection. While it offers a free WordPress plugin for integrity monitoring and malware scanning, its core strength lies in its Website Application Firewall (WAF) and Content Delivery Network (CDN). This approach stops malicious traffic before it ever reaches your server, offering a proactive defense against DDoS attacks, brute-force attempts, and zero-day exploits. It’s an ideal solution for businesses that prioritize performance and want a hands-off, vendor-managed security posture.
Unlike server-side scanners, Sucuri’s WAF acts as a protective shield between your website and the internet, filtering threats at the network edge. This not only enhances security but also significantly reduces server load, often resulting in a noticeable performance boost thanks to its integrated CDN. For businesses already dealing with an infection, Sucuri’s paid plans include professional malware cleanup services with clear service level agreements (SLAs), making it one of the best WordPress security plugins for incident response. If you’re facing an active threat, you can learn more about their professional malware cleanup services.
Leveraging Cloud-Based Protection
To get the full benefit of Sucuri, you must route your website’s traffic through its network by changing your DNS settings (e.g., updating your A records). This step is crucial for activating the WAF. Once configured, the platform requires minimal interaction, as it automatically blocks known threats and virtually patches vulnerabilities. For example, if a major vulnerability is discovered in a popular plugin, Sucuri can deploy a network-level rule to block exploit attempts for all its customers, protecting your site even before you’ve had a chance to update the plugin.
| Key Feature | Why It Matters for Security |
|---|---|
| Cloud-Based WAF/CDN | Stops threats before they hit your server and improves site speed. |
| Malware Cleanup SLA | Guarantees professional malware removal within a set timeframe. |
| DDoS Mitigation | Protects your site from being taken offline by traffic floods. |
| Blacklist Monitoring | Alerts you if your site is flagged by search engines or security authorities. |
- Pros: Offloads security processing from your server, guaranteed cleanup services, significant performance gains via CDN.
- Cons: Core protection requires a paid plan and DNS change, the free plugin has limited functionality compared to the full platform.
Website: https://sucuri.net/
4. SolidWP – Solid Security (formerly iThemes Security)
SolidWP, widely known by its former name iThemes Security, is a veteran in the WordPress security space, offering a comprehensive suite designed for hardening and proactive defense. It has evolved into a key component of the broader Solid Suite, which integrates security with backups and central management. This makes it one of the best WordPress security plugins for users who want a unified, all-in-one solution for site maintenance and protection from a single, reputable provider. Its strength lies in making robust security features like two-factor authentication, brute force protection, and vulnerability monitoring accessible through a clean, user-friendly interface.
The platform’s standout feature is its Patchstack-powered vulnerability scanner, which provides real-time intelligence on outdated plugins or themes and offers virtual patching to secure them before an official fix is available. This proactive approach is critical for preventing zero-day exploits. For example, if a vulnerability is found in “Example Plugin v1.2,” Solid Security can block the specific HTTP requests used to exploit it, keeping you safe while you wait for the developer to release v1.3. This is especially valuable when paired with Solid Backups, reinforcing the idea that a solid security posture requires equally reliable backup and recovery plans.
Hardening and Proactive Defense
Solid Security focuses on preventing unauthorized access and hardening common weak points in a WordPress installation. It automates many security best practices, such as changing default login URLs, enforcing strong passwords, and monitoring for file changes. The login security module is particularly robust, offering modern passkey support alongside traditional two-factor authentication methods to protect against credential stuffing and brute-force attacks.
| Key Feature | Why It Matters for Security |
|---|---|
| Patchstack Vulnerability Scanner | Provides timely alerts and virtual patching for known vulnerabilities. |
| Two-Factor & Passkey Authentication | Secures user logins against compromised passwords. |
| WordPress Hardening | Automatically applies security best practices to reduce the attack surface. |
| Integration with Solid Suite | Combines security with backups and central management for a holistic approach. |
- Pros: Reputable brand history and clear admin UX, powerful vulnerability intelligence via Patchstack, attractive suite pricing when combined with backups.
- Cons: Advanced firewall features are not a cloud WAF, some features are most valuable when used with other SolidWP products.
Website: https://solidwp.com/
5. MalCare
MalCare positions itself as an all-in-one WordPress security solution designed for speed and efficiency, particularly for users managing multiple sites. It combines deep malware scanning with an instant, one-click cleanup feature, aiming to simplify the often-stressful process of recovering a hacked site. Unlike many competitors that rely solely on signature matching, MalCare uses an AI-powered engine to detect complex and new malware by analyzing code behavior. For instance, it can identify a suspicious, obfuscated eval(base64_decode(...)) function that signature-based scanners might miss, making it one of the more technologically advanced options available.
The platform is built with agencies and developers in mind, offering a centralized dashboard to manage security across a portfolio of client websites. Its core value proposition is the promise of quick, reliable malware removal without needing to wait for a support ticket or manual intervention. While the free version offers scanning, the powerful cleanup and firewall features are reserved for its premium tiers, which are priced per site.
Leveraging MalCare’s Cleanup Workflow
The standout feature is its automated cleanup. If a scan detects malware, you can initiate a removal process with a single click directly from the dashboard. The plugin is designed to precisely remove only the malicious code, leaving your legitimate files and database entries untouched, which minimizes the risk of breaking your site during the cleanup. This makes it an excellent emergency tool for those who need a fast and reliable fix.
| Key Feature | Why It Matters for Security |
|---|---|
| 1-Click Instant Malware Removal | Provides rapid, automated cleanup without requiring technical expertise. |
| AI-Powered Malware Scans | Detects new and complex malware that signature-based scanners might miss. |
| Bot Protection & IP Blacklisting | Proactively blocks malicious traffic before it can exploit vulnerabilities. |
| Agency-Friendly Dashboard | Simplifies security management across multiple client websites from one interface. |
- Pros: Extremely fast and efficient cleanup workflow, powerful agency-oriented features and bundles, integrates backups and staging on higher tiers.
- Cons: Full malware removal is a premium feature, the pricing model scales per website which can become costly for large portfolios.
Website: https://www.malcare.com/
6. Jetpack Security (Automattic)
For users who prefer an all-in-one solution from the creators of WordPress.com, Jetpack Security offers a suite of powerful tools tightly integrated into the Automattic ecosystem. It bundles features that are often sold separately, such as real-time backups, malware scanning, and spam protection, making it one of the best WordPress security plugins for those seeking simplicity and reliability. Its core strength lies in leveraging the robust infrastructure of WordPress.com to protect self-hosted sites, providing a seamless and familiar user experience.
Jetpack Security is a paid service, with plans designed to scale. Its standout feature is VaultPress Backups, which performs real-time, incremental backups without slowing down your site. This means every change, from a new post to an e-commerce order, is saved as it happens. Paired with automated malware scanning and one-click fixes, restoring a clean version of your site becomes incredibly straightforward, even for non-technical users. The inclusion of Akismet anti-spam further solidifies its value by keeping comment sections clean.
Leveraging an Integrated Ecosystem
To get the most out of Jetpack, connect it to a WordPress.com account, which unlocks all its features. The dashboard centralizes your security activity, showing scan results, backup status, and an activity log that tracks every change made on your site. For example, if your site is compromised, the activity log might show that an unknown user logged in and modified a plugin file just before the issue occurred. This audit trail is invaluable for pinpointing the source of a breach quickly. For e-commerce stores, the real-time backups ensure no order data is ever lost in the event of a restoration.
| Key Feature | Why It Matters for Security |
|---|---|
| Real-Time Backups (VaultPress) | Ensures no data is lost between scheduled backups; critical for dynamic sites. |
| Automated Malware Scanning | Proactively finds and alerts you to malicious code on your site. |
| One-Click Fixes & Restores | Simplifies the recovery process, minimizing downtime and technical stress. |
| Akismet Anti-Spam | Protects your site from comment spam, a common vector for malicious links. |
- Pros: Seamless integration with Automattic/WordPress.com services, strong backup/restore UX for non-technical teams, all-in-one convenience.
- Cons: Requires connection to a WordPress.com account, can feel bloated if you don’t need all features, storage caps and upsells on lower tiers.
Website: https://jetpack.com/security/
7. WPMU DEV – Defender Pro
WPMU DEV packages its Defender Pro security plugin as part of an all-in-one WordPress platform membership. This model positions it as an excellent choice for agencies, freelancers, or site owners who need a full suite of premium tools- including performance, SEO, backups, and hosting- alongside robust security. Defender Pro handles core security tasks like malware scanning, firewall protection, and two-factor authentication, but its real value is amplified by its integration within the broader WPMU DEV ecosystem.
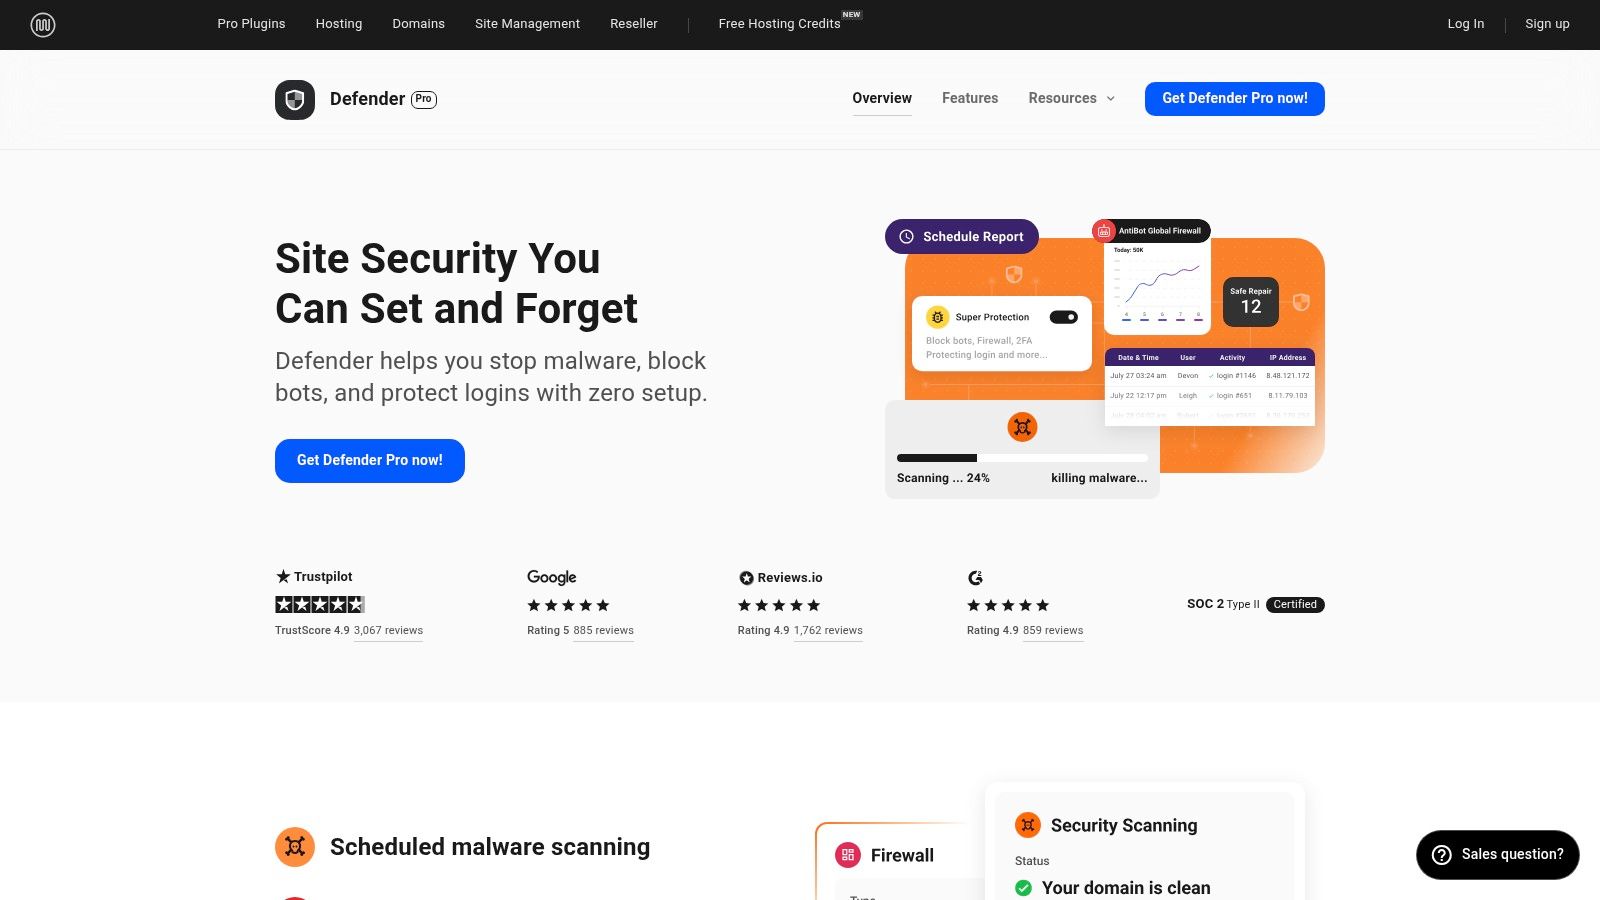
The plugin provides scheduled malware scans with a one-click “Safe Repair” feature, a crowdsourced AntiBot Global Firewall to block known malicious IPs, and detailed audit logging. Its security hardening recommendations are easy to follow, allowing you to disable trackbacks or hide login error messages with a single click. For example, a common recommendation is to disable the file editor in the WordPress dashboard, preventing an attacker who gains admin access from easily modifying theme or plugin code. The primary appeal is getting one of the best WordPress security plugins as part of a bundle that simplifies site management and is backed by 24/7 expert support.
Leveraging the WPMU DEV Ecosystem
The key to maximizing Defender Pro is using it in conjunction with other WPMU DEV services. For instance, you can manage security settings for multiple client sites from a centralized dashboard, “The Hub.” This integrated approach allows you to run scans, implement hardening, and monitor logs across your entire portfolio from one location, offering significant efficiency gains for developers and agencies managing multiple WordPress installations.
| Key Feature | Why It Matters for Security |
|---|---|
| All-in-One Membership | Bundles security with performance, backup, and support tools for comprehensive site management. |
| AntiBot Global Firewall | Uses crowdsourced intelligence from the WPMU DEV network to block malicious bot traffic proactively. |
| Centralized Hub Dashboard | Enables efficient management of security settings and monitoring across multiple websites. |
| One-Click Safe Repair | Simplifies the process of cleaning infected core WordPress files after a malware scan. |
- Pros: Incredible value if you utilize the full WPMU DEV membership suite, excellent 24/7 live support, strong integration with other essential site management tools.
- Cons: Not cost-effective if you only need a standalone security plugin, firewall is less advanced than dedicated WAF providers.
Website: https://wpmudev.com/project/wp-defender/
8. WP Cerber Security
WP Cerber Security provides a hardened, multi-layered defense mechanism that combines a powerful firewall, malware scanner, and robust anti-spam engine into a single, comprehensive package. Unlike plugins that focus on one specific threat, WP Cerber adopts a holistic approach by integrating local server-level protection with cloud-based security features. This makes it an excellent choice for site owners who need to block spam comments, secure login forms, and scan for file changes without juggling multiple tools. Its strength lies in its ability to enforce strict access policies and mitigate threats before they reach your WordPress core.
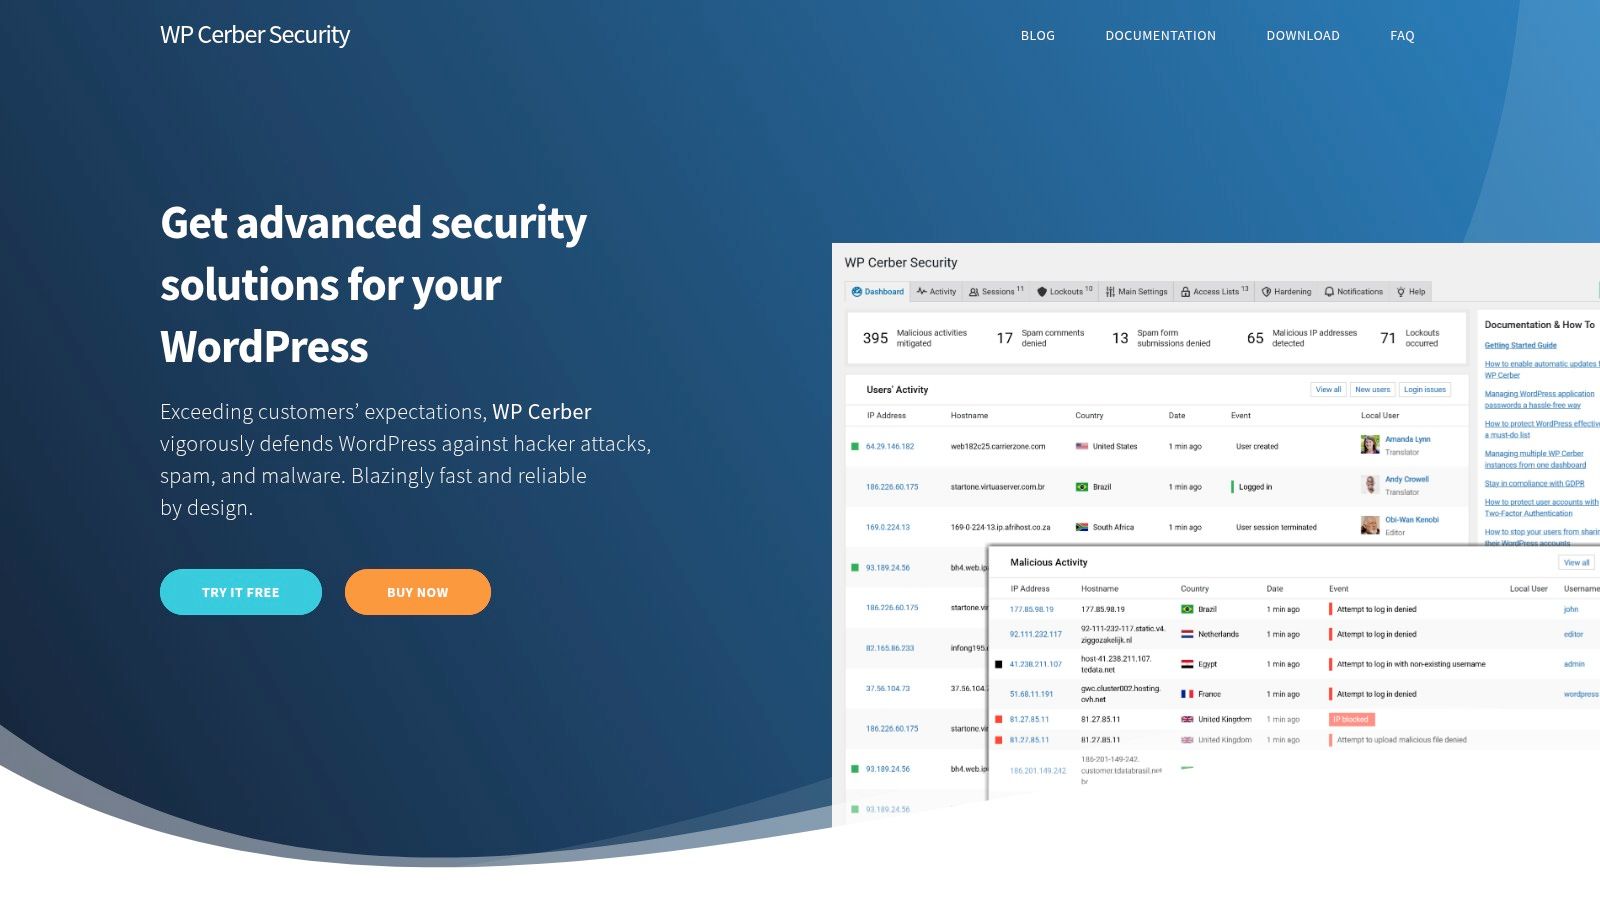
The plugin offers a feature-rich free version that covers essentials like login attempt limits, file integrity monitoring, and a basic firewall. For more advanced protection, the premium version unlocks a cloud-powered firewall, scheduled malware scans, and sophisticated geo-location access rules. The pricing is particularly competitive for users managing multiple websites, offering multi-site packs that provide significant value. This makes WP Cerber one of the best WordPress security plugins for freelancers and agencies needing an affordable, scalable solution.
Using WP Cerber’s Layered Defense
To get the most out of WP Cerber, start by configuring the “Main Settings” to harden your login page, including enabling custom login URLs and limiting login attempts. Next, head to the “Malware Scanner” and perform an initial full scan to establish a baseline for your site’s files. For proactive defense, set up automated daily scans. Finally, use the “Access Lists” to create geo-rules. For example, if your business only operates in North America, you can block all traffic from countries known for high levels of malicious activity, which drastically reduces brute-force attack noise.
| Key Feature | Why It Matters for Security |
|---|---|
| Unified Anti-Spam & Firewall | Reduces plugin bloat by combining two critical security functions. |
| Advanced Malware Scanner | Detects file changes, new files, and malicious code signatures. |
| Geo Access Rules | Blocks traffic from high-risk countries to stop attacks at the source. |
| Login Hardening | Protects against brute-force attacks with lockouts and custom URLs. |
- Pros: Competitive pricing with multi-site packs, combines anti-spam and firewall functionality effectively, strong login protection features.
- Cons: Smaller vendor compared with the largest players, advanced cloud features require paid plans.
Website: https://wpcerber.com/
9. Shield Security (iControlWP)
Shield Security distinguishes itself with a prevention-first philosophy, focusing heavily on robust anti-bot measures and intelligent automation. Instead of just reacting to threats, it aims to block malicious bots before they can cause harm, leveraging technologies like its unique silentCAPTCHA and deep integration with the CrowdSec community blocklist. This makes it one of the best WordPress security plugins for site owners who want to proactively reduce server load and stop attacks at the source.
Developed by the team at iControlWP, Shield Security is built with agencies and multi-site managers in mind, offering flexible licensing that scales from a single site to over one hundred. Its standout feature is the automatic vulnerability scanner, which can be configured to auto-update plugins with known security flaws, providing a critical layer of automated protection. For example, if a vulnerability is reported for “Plugin XYZ,” Shield can automatically apply the update the moment it’s released, closing the window of exposure. This “set and forget” approach appeals to busy administrators who need reliable security without constant manual intervention.
Maximizing Bot Defense and Automation
To get the most out of Shield, enable its bot detection features immediately, including the login guard and silentCAPTCHA for comment forms. This user-friendly CAPTCHA works in the background without requiring visitors to solve puzzles, effectively blocking spam bots while preserving the user experience. For agencies, linking Shield to an iControlWP account unlocks centralized management, allowing you to monitor and apply security policies across your entire portfolio from a single dashboard.
| Key Feature | Why It Matters for Security |
|---|---|
| silentCAPTCHA & Bot Defenses | Blocks malicious bots and spam without frustrating human users. |
| CrowdSec IP Blocklist | Leverages a community-sourced list of malicious IPs for proactive blocking. |
| Vulnerability Auto-Updates | Automatically patches vulnerable plugins, closing security holes quickly. |
| Multi-Site & Portfolio Tools | Centralizes security management for agencies and developers. |
- Pros: Strong focus on proactive bot prevention, flexible licensing for agencies, automated vulnerability patching.
- Cons: Some advanced features are reserved for premium tiers, the connection to iControlWP can be confusing initially.
Website: https://getshieldsecurity.com/
10. AIOS – All-In-One Security (Team Updraft/UpdraftPlus)
Developed by the trusted team behind UpdraftPlus, AIOS – All-In-One Security offers a comprehensive and user-friendly approach to hardening WordPress. It stands out by simplifying complex security settings through a grading system and categorized feature sets, making it one of the best WordPress security plugins for users who want clear, actionable steps. The plugin’s dashboard presents a security strength score, motivating administrators to implement recommended firewall rules, login defenses, and file system protections to improve their site’s posture.
AIOS excels at providing robust foundational security for free, including brute-force login protection, a Web Application Firewall (WAF), and user account monitoring. While many core features are available in the free version, upgrading to Premium unlocks more advanced capabilities like automated malware scanning, two-factor authentication (2FA), and country blocking. This freemium model allows small sites to establish a strong baseline defense at no cost while providing a clear upgrade path as their security needs grow.
Getting Started with AIOS
Upon activation, navigate to the AIOS dashboard and review your initial security score. The plugin guides you through critical, intermediate, and advanced settings. A good starting point is activating the “Basic Firewall Protection” and configuring “Brute Force” settings to limit login attempts. For example, setting login lockdown after three failed attempts and blocking the IP for 24 hours is a highly effective first step. This simple rule can stop the vast majority of automated password-guessing attacks.
| Key Feature | Why It Matters for Security |
|---|---|
| Security Strength Meter | Gamifies security improvements by providing a clear score. |
| Login Lockdown | Actively blocks brute-force attacks by locking out suspicious IPs. |
| Web Application Firewall | Provides a critical first line of defense against common exploits. |
| Premium Malware Scanning | Automates the detection of malicious code within your core files. |
- Pros: Strong documentation and support from the Updraft team, cost-competitive pricing, user-friendly interface with a security score.
- Cons: Key features like malware scans and country blocking are premium-only, may require deactivating overlapping security plugins to avoid conflicts.
Website: https://aiosplugin.com/
11. Security Ninja
Security Ninja positions itself as a proactive security testing and hardening tool, distinguishing itself by running over 50 security tests to identify vulnerabilities before attackers do. Instead of just reacting to threats, it helps you perform a security audit on your core files, plugins, and server settings, offering one-click fixes for many issues it finds. This preventative approach makes it one of the best WordPress security plugins for developers and agencies who want to lock down a site from the very beginning. It combines this with essential real-time protections like a firewall, malware scanner, and brute-force blocker.
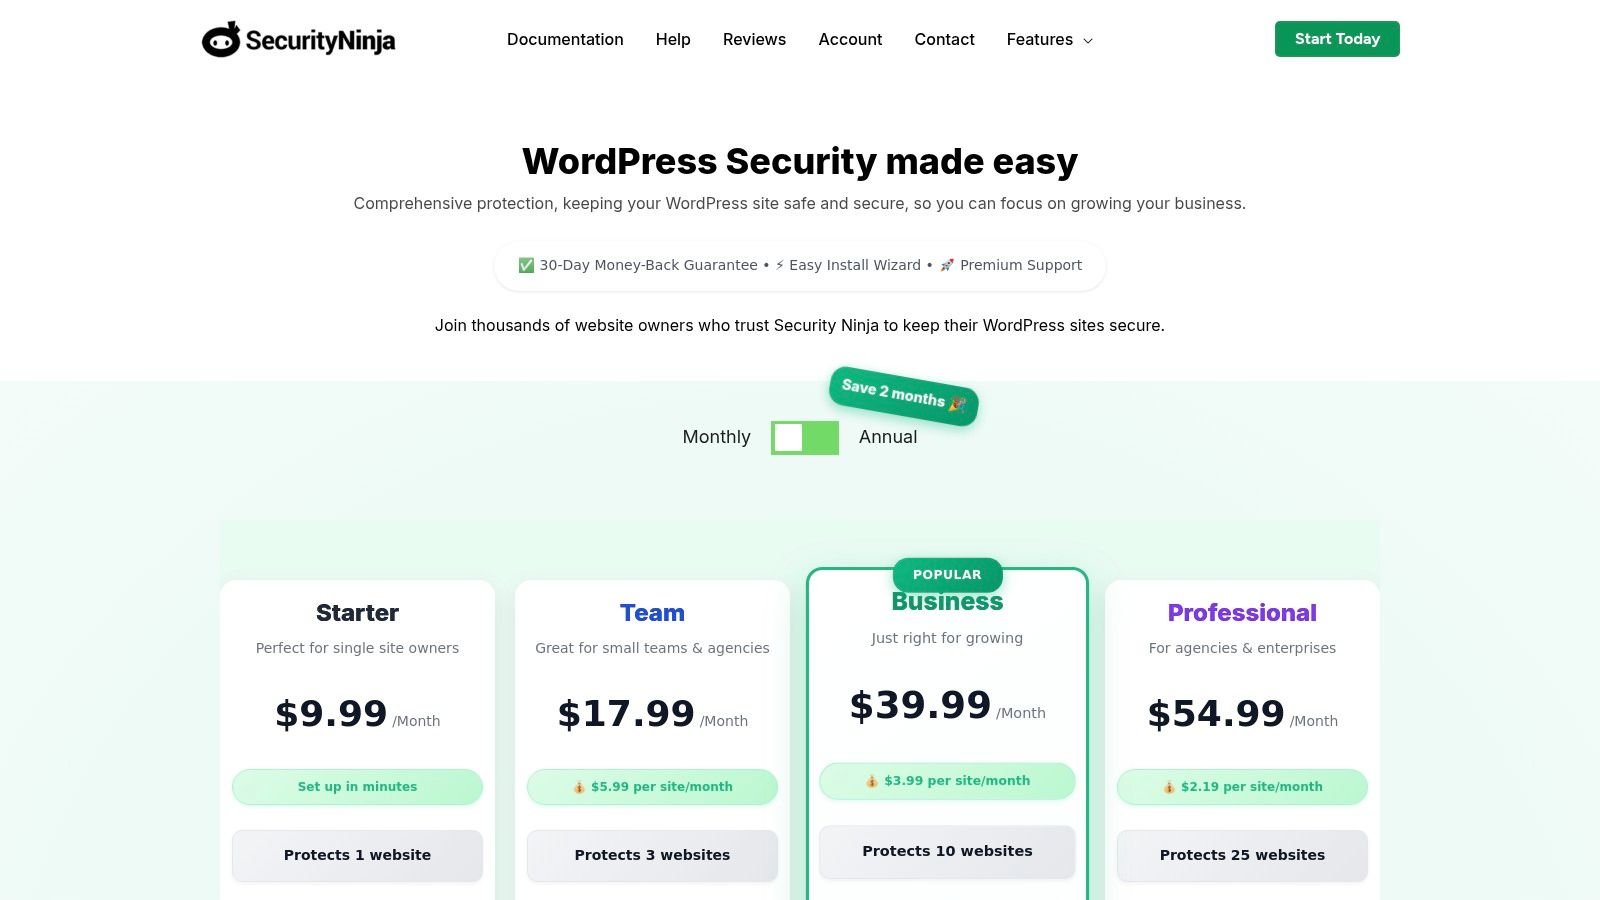
What makes Security Ninja particularly compelling are its agency-focused features. It offers multi-site and MainWP bundles, complete with white-labeling options, allowing developers to offer branded security services to their clients. The setup wizard is straightforward, guiding users through the initial scan and hardening process without overwhelming them. While it doesn’t offer its own cloud-based WAF, it’s designed to work alongside existing host-level or third-party firewalls, focusing instead on comprehensive on-site vulnerability checks and immediate hardening.
Mastering Proactive Security Audits
To get the most value, run the main security test immediately after installation. This generates a detailed report with a security score and a list of passed, failed, and warning tests. For example, it might flag that your site has wp-config.php file permissions set to 777 (world-writable), a critical vulnerability. Go through the failed tests one by one; many, like disabling file editors, can be fixed with a single click directly from the dashboard. Schedule these scans to run automatically every week to catch any new vulnerabilities introduced by plugin updates or configuration changes.
| Key Feature | Why It Matters for Security |
|---|---|
| 50+ Security Tests | Audits your site for known vulnerabilities and misconfigurations. |
| One-Click Auto Fixes | Simplifies the hardening process for non-technical users. |
| Agency & White-Labeling | Allows developers to offer branded security management to clients. |
| Event Logger | Tracks all changes on the site to quickly identify suspicious activity. |
- Pros: Straightforward setup wizard, strong focus on proactive hardening, agency-friendly licensing and white-label options.
- Cons: Does not provide its own dedicated cloud WAF, smaller user base compared to market leaders.
Website: https://wpsecurityninja.com/pricing/
12. NinjaFirewall (NinTechNet)
NinjaFirewall operates differently from most security plugins by functioning as a true Web Application Firewall (WAF) that filters traffic before it even reaches WordPress. This standalone firewall inspects incoming HTTP requests at the earliest possible stage, blocking malicious bots, scanners, and exploit attempts before they can consume server resources or interact with vulnerable plugin code. Its primary advantage is this pre-emptive, performance-sensitive approach to threat mitigation.
The plugin offers a robust free version (WP Edition) on the WordPress.org directory, which provides significant protection. For more advanced features, the paid WP+ edition, available directly from the NinTechNet website, offers more granular policies and even earlier-stage request filtering. NinjaFirewall is highly technical, providing detailed logs and extensive customization options that appeal to developers and security-conscious administrators who want precise control over their site’s defense rules.
Mastering Early-Stage Filtering
To get the most out of NinjaFirewall, it’s essential to understand its logging system. The “Firewall Log” provides a real-time view of all blocked requests, including the reason for the block and the specific rule that was triggered. For example, you might see it blocked an attempt to access xmlrpc.php, a common target for brute-force attacks. Reviewing this log helps you understand the types of threats your site faces and allows you to whitelist legitimate requests that may be incorrectly flagged. The documentation-driven setup is more hands-on but rewards users with a highly efficient security layer.
| Key Feature | Why It Matters for Security |
|---|---|
| True WAF Functionality | Filters traffic before WordPress loads, stopping threats at the server level for better performance and security. |
| Virtual Patching | Protects against known vulnerabilities in plugins and themes, even before official patches are released. |
| Advanced Brute-Force Protection | Secures the login page with multiple layers of defense beyond simple IP blocking. |
| Detailed Event Logging | Offers deep visibility into all security events, helping diagnose attacks and fine-tune firewall rules. |
- Pros: Lightweight, high-performance blocking before WordPress initializes; highly effective against a wide range of attacks; powerful free version available.
- Cons: Less beginner-friendly than all-in-one solutions; setup can be more complex; the premium version is sold outside of mainstream marketplaces.
Website: https://nintechnet.com/
Top 12 WordPress Security Plugins — Feature Comparison
| Solution | Core features ✨ | UX / Quality ★ | Price / Value 💰 | Target 👥 | USP 🏆 |
|---|---|---|---|---|---|
| WordPress.org Plugin Directory | ✨ Centralized listings, reviews, install counts, changelogs | ★★★☆☆ (varies by plugin) | 💰 Free discovery & install | 👥 Site owners researching plugins | 🏆 Authoritative catalog for vetting plugins |
| Wordfence (Defiant Inc.) | ✨ Endpoint firewall, malware scanner, IP blocking, central management | ★★★★☆ (mature, widely used) | 💰 Free → Premium / Care / Response (per-site licensing) | 👥 Sites needing on-site, deep protection | 🏆 Robust endpoint firewall & research team |
| Sucuri | ✨ Cloud WAF/CDN, malware cleanup, DDoS mitigation, blacklist removal | ★★★★☆ (edge protection + SLAs) | 💰 Paid tiers (WAF requires DNS change) | 👥 Sites wanting vendor-handled edge protection | 🏆 Cloud WAF + rapid malware removal SLAs |
| SolidWP – Solid Security | ✨ Hardening, 2FA/passkeys, Patchstack virtual patching, scans | ★★★★☆ (clear UX, reputable) | 💰 Suite pricing (bundled backups/management) | 👥 Businesses wanting integrated suite | 🏆 Patchstack-driven vulnerability intelligence |
| MalCare | ✨ AI scans, 1‑click malware removal, bot/geoblocking | ★★★★☆ (fast cleanup workflows) | 💰 Premium for full cleanup; scales by site count | 👥 Agencies & sites needing fast remediation | 🏆 Instant AI-assisted malware removal |
| Jetpack Security (Automattic) | ✨ Real-time backups, malware scans, WAF, anti-spam | ★★★★☆ (seamless Automattic integration) | 💰 Paid tiers (requires WordPress.com) | 👥 Non-technical teams wanting simple restores | 🏆 Integrated backups + one-click restore UX |
| WPMU DEV – Defender Pro | ✨ Malware scans, audit logs, 2FA, crowdsourced firewall | ★★★★☆ (strong docs & support) | 💰 Membership-based (bundled value) | 👥 Agencies / teams needing multi-tool bundles | 🏆 Best value when bundled with performance & support |
| WP Cerber Security | ✨ Layered local/cloud protection, integrity scans, geo rules | ★★★★☆ (competitive, reliable) | 💰 Competitive multi-site packs | 👥 Multi-site owners on a budget | 🏆 Effective anti-spam + firewall combo |
| Shield Security (iControlWP) | ✨ silentCAPTCHA, CrowdSec integration, auto-updates, portfolio tools | ★★★★☆ (prevention-first) | 💰 Flexible licensing (1–100+ sites) | 👥 Agencies & portfolio managers | 🏆 Strong anti-bot focus + flexible licensing |
| AIOS – All-In-One Security | ✨ Login defense, firewall, security score, audit logs | ★★★★☆ (good docs, cost-competitive) | 💰 Premium for scans/geo-blocking | 👥 Cost-conscious admins & SMBs | 🏆 Clear guidance levels + security scoring |
| Security Ninja | ✨ 50+ security tests, one-click fixes, white‑label & agency bundles | ★★★★☆ (straightforward, agency-friendly) | 💰 Per-site or agency bundles | 👥 Agencies / white-label providers | 🏆 Extensive tests + white‑label options |
| NinjaFirewall (NinTechNet) | ✨ Pre-WordPress request filtering, virtual patching, detailed logs | ★★★★☆ (lightweight, performance-sensitive) | 💰 Free WP edition; paid WP+ via vendor | 👥 Sites needing early-stage WAF filtering | 🏆 True pre‑application WAF (early request blocking) |
Frequently Asked Questions (FAQs)
Do I really need a WordPress security plugin?
Yes, absolutely. While WordPress core software is secure, vulnerabilities are frequently introduced through third-party plugins and themes. A security plugin acts as a crucial layer of defense, providing a firewall to block attacks, a scanner to detect malware, and tools to harden your site against common exploits like brute-force login attempts. Without one, your site is a much easier target for automated attacks.
Can a security plugin slow down my website?
It’s possible, but the best WordPress security plugins are designed to minimize performance impact. Cloud-based WAFs like Sucuri actually speed up your site by offloading security tasks and providing a CDN. Server-side plugins like Wordfence or NinjaFirewall are highly optimized, and any minor performance cost is a worthwhile trade-off for the protection they provide. The key is to configure them properly, for example, by scheduling scans during off-peak hours.
What’s the difference between a cloud WAF and an endpoint firewall?
An endpoint (or application-level) firewall, like the one in Wordfence, runs on your server as part of your WordPress installation. It inspects traffic after it has reached your hosting environment. A cloud-based WAF, like Sucuri’s, sits between your site and the internet, filtering traffic at the network edge before it ever touches your server. Cloud WAFs are generally better at mitigating large-scale DDoS attacks and have less impact on server performance.
Is a free security plugin good enough?
For many small blogs or personal websites, a high-quality free plugin like Wordfence or the free version of AIOS can provide a strong baseline of protection. They typically offer essential features like login protection and basic malware scanning. However, for business, e-commerce, or mission-critical websites, a premium plugin is a wise investment. Premium features often include real-time threat intelligence, guaranteed malware removal, virtual patching, and faster support, which are vital for minimizing downtime and risk.
How many security plugins should I install?
One. You should only use one comprehensive security plugin at a time. Installing multiple security plugins that offer similar features (like two different firewalls) can cause conflicts, lead to performance issues, or even lock you out of your own site. It’s better to choose one robust solution that meets all your needs than to try and piece together several smaller ones.
Moving from Defense to Dominance: Your Next Steps in Web Security
We’ve journeyed through an extensive lineup of the best WordPress security plugins available today. From the comprehensive, all-encompassing protection of Wordfence and Sucuri to the specialized, performance-focused approach of NinjaFirewall and the user-friendly interface of AIOS, it’s clear there is no one-size-fits-all solution. Your ideal plugin is not necessarily the one with the most features, but the one that aligns perfectly with your website’s specific risk profile, technical resources, and budget.
The core lesson is that web security is not a passive, “set it and forget it” task. It is an active, ongoing discipline. Installing a powerful plugin is the foundational first step, but the real work involves a strategic combination of technology, process, and vigilance. This moves you beyond a simple defensive posture into a state of security dominance, where you are in control of your digital environment.
Key Takeaways and Choosing Your Path Forward
Making the right choice requires a clear-eyed assessment of your needs. Let’s distill the decision-making process into actionable steps:
For E-commerce and High-Transaction Sites: Your primary concern is the integrity of customer data and uptime. A Web Application Firewall (WAF) is non-negotiable. Look to solutions like Sucuri or MalCare, which offer robust, cloud-based WAFs that filter traffic before it even reaches your server, minimizing performance impact and providing a powerful first line of defense against attacks like SQL injections and cross-site scripting.
For Small Businesses and Bloggers: You need a balance of comprehensive features, ease of use, and affordability. Plugins like Wordfence (Free), AIOS, or SolidWP – Solid Security offer an excellent starting point. They provide essential hardening measures, malware scanning, and login protection that cover the most common threats without requiring a deep technical background to configure.
For Performance-Conscious Users: If every millisecond of load time counts, a server-level firewall is your best bet. NinjaFirewall stands out here, as its script-level integration allows it to act before WordPress even loads, offering top-tier protection with minimal performance overhead. Similarly, Shield Security is built with a focus on smart, efficient protection that avoids resource-heavy scans.
Beyond the Plugin: Building a Resilient Security Ecosystem
Remember, even the best WordPress security plugins are just one component of a holistic security strategy. True resilience is built on multiple layers of protection. As you implement your chosen plugin, consider these critical, complementary actions:
Develop an Action Plan: What happens if, despite your best efforts, a breach occurs? Panic is not a strategy. To truly achieve dominance in web security, organizations must also develop a robust security incident response plan to quickly and effectively manage any potential breaches. This document outlines roles, communication procedures, and technical steps to contain the threat, assess the damage, and restore operations efficiently.
Prioritize Proactive Maintenance: Your plugin is only as effective as the environment it protects. This means consistently updating the WordPress core, all themes, and all other plugins. Outdated software is the single most common entry point for attackers.
Implement a Backup Strategy: Security and backups are two sides of the same coin. A reliable, off-site backup solution (like UpdraftPlus or a host-level service) is your ultimate safety net, allowing you to restore a clean version of your site in a worst-case scenario.
Ultimately, selecting and configuring one of these top-tier plugins is a major step toward securing your digital assets. It transforms your website from a soft target into a hardened fortress, giving you the confidence to grow your business online.
Choosing, configuring, and managing the best WordPress security plugins on top of daily business operations can be overwhelming. At Websites USA, we provide comprehensive website management that integrates expert security hardening, performance optimization, and proactive maintenance. We turn your website into a secure, high-performing asset so you can focus on running your business, not fighting technical fires.


