
A solid back up strategy isn't merely an IT task—it's the definitive insurance policy for your digital assets. In expert terms, it's about creating redundant, recoverable copies of your data and storing them across multiple secure locations. This ensures you can restore operations and maintain business continuity after a hardware failure, a sophisticated cyberattack, or simple human error without catastrophic consequences for your business.
Why a Backup Plan Is Your Business Lifeline
Imagine your entire e-commerce platform—product catalogs, customer transaction histories, proprietary content—is suddenly gone. For businesses operating without a robust data protection plan, this isn't a hypothetical nightmare; it's an imminent risk. A well-architected backup strategy is not an administrative chore; it is a foundational component of corporate survival and risk management.
Think of it as your ultimate operational fail-safe. Whether you are facing a critical server crash, a ransomware attack that has encrypted your live data, or an employee accidentally deleting a production database, a reliable backup system is what distinguishes a manageable incident from a business-ending disaster.
The Real Price of Losing Your Data
When your website data is compromised, the impact extends far beyond a temporarily unavailable site. The operational and financial fallout can permeate every aspect of your business, from immediate revenue streams to long-term brand equity.
Without a recovery plan, you’re not just looking at lost sales from downtime. You’re risking long-term damage to your brand and the trust you’ve spent years building with your customers.
Let's quantify the stakes with concrete examples:
- Serious Revenue Loss: For an e-commerce site generating $10,000 per day, even four hours of downtime translates to over $1,600 in direct lost revenue, not including the long-tail impact of abandoned carts and frustrated customers.
- Reputation Damage: A website that is frequently offline or loses customer data signals unreliability. A 2022 survey showed that 88% of online consumers are less likely to return to a site after a bad experience, making downtime a critical customer retention issue.
- Data Gone for Good: A catastrophic hardware failure (like a RAID array corruption) or a targeted wiper-style malware attack can result in the permanent, irrecoverable loss of all data if no external backup exists.
The Growing Data Problem for Small Businesses
Businesses are creating and storing data at an exponential rate. By 2025, global data creation is projected to exceed 175 zettabytes, with a significant portion managed by cloud services. For small and medium-sized businesses, this data proliferation magnifies a critical vulnerability. Industry reports indicate that a shockingly small fraction of business data is adequately backed up, leaving countless digital operations dangerously exposed.
This is precisely why a structured, documented backup plan is essential. Proactive data protection isn't a luxury reserved for large corporations; it's a fundamental principle of sound business management. Backups must be integrated into routine operations with the same diligence as financial accounting or inventory management.
To understand how this fits into a broader operational context, it's worth exploring the expert reasons why your business needs a website maintenance package. A robust backup plan is the non-negotiable cornerstone of any professional maintenance strategy.
Understanding the Language of Data Recovery
Before you can architect a resilient backup strategy, you must be fluent in the core terminology. This isn't about memorizing technical jargon; it's about defining the precise business requirements that will dictate your entire recovery framework.
Let's demystify the two most critical metrics in data recovery: Recovery Time Objective (RTO) and Recovery Point Objective (RPO). Think of these not as IT metrics, but as business-level service agreements you make with yourself and your customers during a crisis.
RTO: The Speed of Your Comeback
Your Recovery Time Objective (RTO) answers a direct business question: "What is the absolute maximum time we can afford to be offline following a disaster before severe business damage occurs?"
This metric is exclusively about downtime. RTO is the targeted duration within which a business process must be restored after a disaster to avoid unacceptable consequences. For an e-commerce store, a short RTO—for example, one hour—is critical, as every minute offline corresponds to lost sales and potential customer churn. This necessitates a high-availability solution, such as hot-site failover. Conversely, an internal marketing blog might have a 24-hour RTO, allowing for a more standard, less costly restoration process.
RPO: The Acceptable Data Loss
Next is the Recovery Point Objective (RPO). It answers an equally crucial, but distinct, question: "What is the maximum amount of data, measured in time, that we can afford to lose and recreate manually?"
This metric dictates your required backup frequency. A busy online store processing dozens of orders per hour might set an RPO of 15 minutes. This means the business cannot tolerate losing more than 15 minutes of transactional data, requiring backups or database transaction log shipping to occur at that interval. In contrast, a company blog updated weekly could easily sustain an RPO of 24 hours, making a single daily backup sufficient.
Key Takeaway: Your RTO dictates how much downtime you can handle, while your RPO dictates how much data loss you can handle. Getting these two numbers right is the secret to a backup plan that actually works for your business.
To make this crystal clear, let’s look at how RTO and RPO translate to real-world business decisions.
RTO vs. RPO: What Every Business Owner Needs to Know
This table breaks down the core difference between these two critical concepts.
| Concept | Business Question It Answers | Example Metric | Primary Impact |
|---|---|---|---|
| RTO | "How quickly must we recover?" | 1 Hour | Downtime. Defines the urgency of your recovery process and the technology needed to meet that speed. |
| RPO | "How much data can we afford to lose?" | 15 Minutes | Data Loss. Defines your backup frequency and how much manual work you'd have to redo after a failure. |
Ultimately, a low RTO protects your revenue stream by minimizing downtime, while a low RPO protects your operational integrity by minimizing data loss. You need to decide the right balance for your specific business.
Clarifying Retention Policies
Finally, let's touch on retention policies. This defines the lifecycle of your backup data—how long you keep specific backup sets before they are permanently deleted. Storing every backup indefinitely is not only cost-prohibitive but also creates a data management nightmare.
A strategic retention policy uses a tiered model known as Grandfather-Father-Son (GFS). A typical GFS scheme for a business website might look like this:
- Daily Backups (Son): Retained for 7 days. Used for rapid recovery from common operational errors, like accidental file deletion or a failed plugin update.
- Weekly Backups (Father): Retained for 4 weeks. Provides a broader set of recovery points if an issue goes unnoticed for several days.
- Monthly Backups (Grandfather): Retained for 12 months. Serves as a long-term archive for historical data analysis, compliance audits, or legal discovery.
This structure provides a comprehensive safety net for various recovery scenarios while optimizing storage costs. Once your RTO, RPO, and retention policies are defined, you have the strategic foundation for a truly resilient business.
Choosing the Right Backup Method for Your Needs
Not all backup methodologies are created equal. The optimal strategy for your website involves a calculated trade-off between backup speed, storage consumption, and restoration complexity. Think of your data as a critical financial ledger; each method is a different way of auditing and securing its history.
The goal is to select a method that aligns with your site's data change rate (velocity), your budget, and your defined RPO. Let’s dissect the primary backup types.
Full Backups: Your Complete Safety Copy
A full backup is an exact, complete copy of the entire dataset at a point in time. It is the baseline against which all other backup types are measured. It’s the simplest and most foolproof method because restoration is a single-step process: you restore the one complete backup file.
- Example: A weekly full backup of a 50 GB website captures all 50 GB of files and database tables.
- Pros: Simple to manage and offers the fastest, most reliable restoration process.
- Cons: Consumes the most storage space and takes the longest to complete, making it impractical for frequent execution on large datasets.
Incremental Backups: Small and Speedy Updates
An incremental backup captures only the data blocks that have changed since the last backup of any type (full or incremental). This approach is highly efficient in terms of speed and storage.
- Example: After a Sunday full backup, Monday's incremental backup might be only 500 MB. Tuesday's incremental would capture only the changes made on Tuesday, perhaps another 300 MB.
- Pros: Extremely fast backup windows and minimal storage use.
- Cons: Restoration is complex and slow. To fully recover, you need the last full backup plus every subsequent incremental backup in the correct, unbroken sequence. The failure of a single incremental file can invalidate the entire recovery chain.
Differential Backups: The Balanced Approach
A differential backup is a strategic hybrid. It saves all the data that has changed since the last full backup. Each subsequent differential backup grows larger as it accumulates all changes since that last full baseline.
- Example: After Sunday's full backup, Monday's differential captures Monday's changes (500 MB). Tuesday's differential captures all changes from both Monday and Tuesday (e.g., 800 MB).
- Pros: Faster restoration than incremental, requiring only two files: the last full backup and the most recent differential. It provides a good balance between storage use and recovery speed.
- Cons: Uses more storage than incremental backups and backup windows lengthen over the course of the week.
For a deeper dive, this practical guide to differential and incremental backups really breaks down the technical pros and cons.
The image below shows how your business needs—specifically your tolerance for downtime (RTO) and data loss (RPO)—should drive your entire recovery plan.
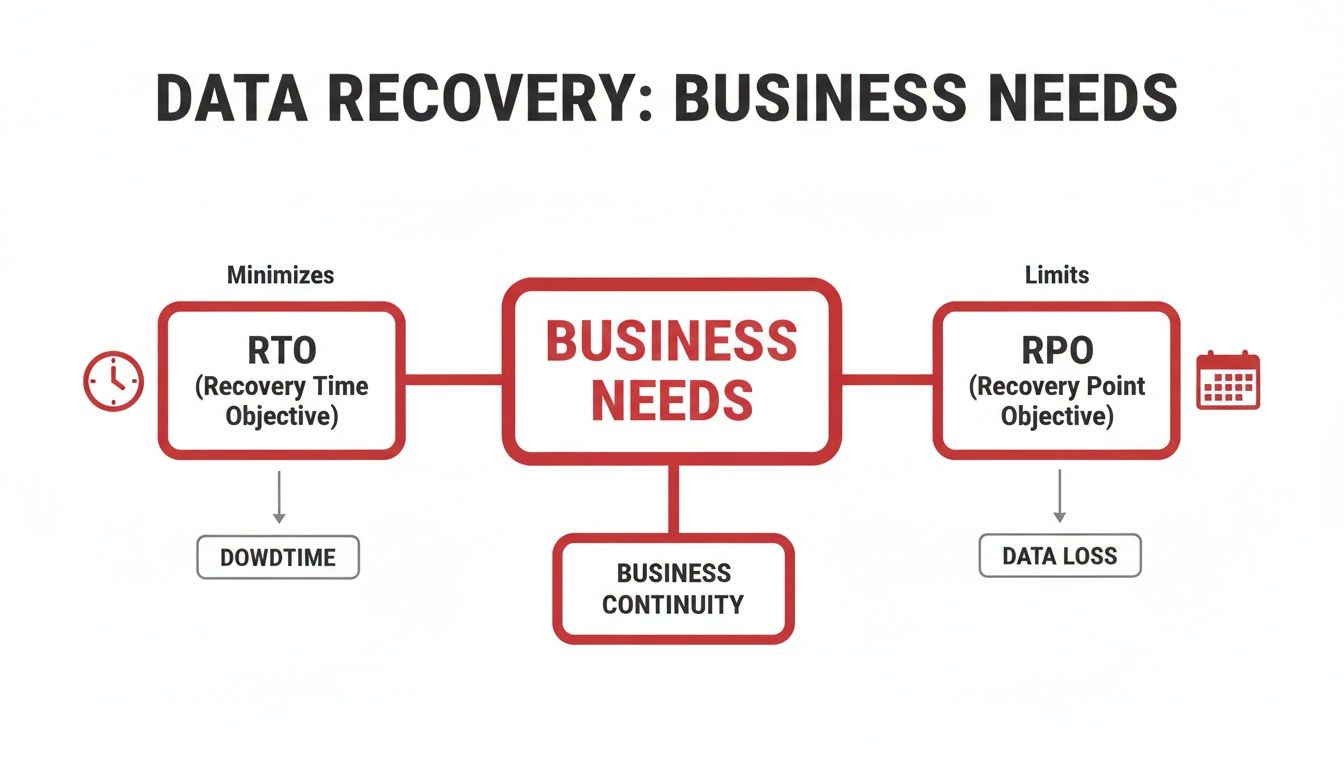
As you can see, figuring out your RTO and RPO is the first and most important step in building a strategy that actually works for your business.
Going Beyond the Basics with Snapshots and Versioning
Modern backup strategies often include more advanced tools that give you even more flexibility, especially if you’re running a dynamic website.
Key Insight: Combining traditional methods with newer concepts like versioning and snapshots creates a multi-layered defense that is both efficient and highly resilient against data loss.
Here are two important concepts to know:
- Versioning: This practice retains multiple past versions of a backup, allowing you to restore to various points in time. For instance, if you discover a database corruption that occurred three days ago, versioning lets you "roll back" to a clean version from four days ago, bypassing the corrupt data entirely.
- Snapshots: A snapshot is an instantaneous, point-in-time "photograph" of a file system or volume. Unlike file-based backups, snapshots are block-level and incredibly fast to create. They are ideal for creating quick recovery points before performing high-risk actions, such as a major WordPress core update or server migration.
Where to Store Your Backups for Maximum Security
Selecting the right backup methodology is only half the equation. The physical and logical location of your backup repositories is equally critical for building a truly resilient recovery plan. The storage strategy directly impacts recovery speed (RTO), security, and resilience against site-wide disasters.
Let's evaluate the primary storage models: onsite, offsite, and cloud.
Onsite Backups For Lightning-Fast Recovery
An onsite backup is a copy of your data stored locally, within your physical business premises. This is typically on a separate device from the production server, such as an external hard drive, a dedicated backup server, or a Network Attached Storage (NAS) device.
The primary advantage is speed.
Restoring data over a local network (LAN) is orders of magnitude faster than downloading it from the internet. This makes onsite backups invaluable for meeting aggressive RTOs where minimizing downtime is the top priority.
However, it introduces a significant single point of failure.
A fire, flood, or theft that hits your primary systems will almost certainly take out your onsite backups along with them, leaving you with nothing. Think of onsite storage as your crucial first line of defense, but never, ever your only one.
Offsite and Cloud Backups: The Ultimate Safety Net
To mitigate the risk of a localized disaster, a geographically separate backup copy is non-negotiable. This is the core principle of offsite backups.
Historically, this involved physically transporting tapes or drives to a secure location. Today, cloud storage services have automated this process, making it more efficient and reliable.
Cloud backup services from providers like Amazon Web Services (AWS), Google Cloud, or Backblaze offer geographic redundancy by default, storing your data in highly secure, geographically dispersed data centers. This instantly decouples your backup's safety from your primary business location.
Cloud storage offers several key advantages for modern businesses:
- Scalability: Storage capacity can be scaled on demand, eliminating the need for upfront hardware investment.
- Accessibility: Backups can be accessed from any location with an internet connection, facilitating disaster recovery to new hardware or a different cloud provider.
- Resilience: Cloud providers build in multiple layers of redundancy for power, cooling, and connectivity, offering durability far beyond what most businesses could achieve on their own.
While cloud solutions are powerful, remember they are just one piece of the puzzle. For a deeper dive, our guide on website security best practices offers great insights that pair perfectly with a solid backup plan.
The 3-2-1 Rule: Your Blueprint for Resilience
The debate isn't about onsite vs. offsite vs. cloud; the expert answer is a strategic combination of them, guided by the industry-standard 3-2-1 rule. This simple yet powerful framework provides a blueprint for comprehensive data protection.
The rule dictates:
- Maintain at least THREE total copies of your data (your primary production data plus two backups).
- Store your copies on TWO different types of media (e.g., internal server disks and cloud object storage).
- Keep ONE of those copies in an offsite location.
Here’s a practical implementation for a business website:
- Copy 1 (Production): The live website data on your web server's primary storage.
- Copy 2 (Onsite): A nightly backup to a local NAS device in your office. This copy is on different media and enables rapid local restores.
- Copy 3 (Offsite): The same nightly backup is automatically replicated to a secure cloud storage provider, insulating it from any local disaster.
Adhering to the 3-2-1 rule creates a defense-in-depth strategy, leveraging the speed of local backups and the security of an offsite copy. It ensures that no single failure event can result in total data loss.
Building Your Custom Backup Strategy Blueprint
Understanding the theory of RTOs and backup types is one thing; applying it to create a functional, cost-effective plan for your specific business is the real challenge. A backup strategy designed for a static brochure website would be grossly inadequate for a dynamic e-commerce operation.
You need a blueprint tailored to your operational tempo, budget, and risk tolerance. Below are two common business scenarios, serving as expert templates you can adapt for your own needs.
Blueprint 1: The Simple Brochure WordPress Site
This plan is optimized for websites with low data velocity—sites that are not frequently updated. Examples include local service businesses, consultants, or online portfolios. The primary objective is simple: recover from common issues like plugin conflicts, failed updates, or user error.
Core Strategy Components:
- Backup Frequency: A weekly full backup is sufficient. This captures all content changes without creating excessive storage overhead. For example, a backup job scheduled to run every Sunday at 2 AM.
- Storage Location: A simplified 3-2-1 approach. One copy is stored on the web host's server (if offered) for convenience, with a second, primary copy automatically sent to an offsite cloud service like Google Drive or Dropbox.
- Retention Schedule: A simple rolling schedule: retain the last four weekly backups. This provides a one-month recovery window, which is ample for this use case.
- Target RTO/RPO: The objectives are moderate. An RTO of 24 hours is acceptable, as a day of downtime for a non-transactional site is not a financial catastrophe. The RPO is 7 days, aligning with the weekly backup schedule.
Blueprint 2: The High-Traffic E-commerce Store
For an online store, the stakes are exponentially higher. Downtime directly translates to lost revenue, and data loss means losing customer orders, creating a logistical and reputational crisis. This blueprint prioritizes business continuity and data integrity above all else.
This aggressive strategy is built around a demanding RPO of under 30 minutes, ensuring that even in a worst-case scenario, you never lose more than a handful of customer orders. Protecting transactional data is the number one priority.
Core Strategy Components:
- Backup Frequency: A multi-tiered schedule is required. Daily full backups of the entire site (files and database) are the baseline. Critically, the transactional database must be backed up far more frequently—for instance, every 15-30 minutes using incremental backups or real-time transaction log shipping.
- Storage Location: A strict 3-2-1 implementation is mandatory. Backups are stored locally on a separate device for fast restores, with replicas sent to a primary cloud provider (Amazon S3) and a secondary, different cloud provider for complete redundancy against a provider outage.
- Retention Schedule: A more sophisticated GFS policy is needed:
- Retain all 15-minute database backups for 48 hours.
- Retain daily full backups for 14 days.
- Retain weekly backups for 3 months.
- Retain one monthly backup for 1 year for financial auditing and archival.
- Target RTO/RPO: The objectives are stringent. The RTO must be under 1 hour, requiring a well-rehearsed recovery plan. The RPO is 30 minutes or less to minimize the loss of critical order data.
Let's put these two strategies side-by-side to see just how different they are.
Backup Strategy Blueprint Comparison
This side-by-side view really highlights how a website's purpose should dictate its protection plan.
| Requirement | Brochure WordPress Site | E-commerce WordPress Site |
|---|---|---|
| RPO (Max Data Loss) | 7 Days | Under 30 Minutes |
| RTO (Max Downtime) | 24 Hours | Under 1 Hour |
| Backup Frequency | Weekly Full Backup | Daily Full + 15-Min Database Backups |
| Storage Method | Host Server + Offsite Cloud | Local + Dual Offsite Cloud Providers |
| Retention Policy | 4 Weekly Backups | Tiered (Daily, Weekly, Monthly) |
As you can see, there's no such thing as a "one-size-fits-all" backup plan. The right strategy always starts with understanding what you stand to lose.
Testing and Automating Your Defense Plan

An untested backup strategy is not a plan; it's a liability. The final and most critical phase is to operationalize your blueprint through automation and validate it with rigorous testing. This is where a theoretical plan becomes a reliable, battle-hardened recovery system.
The first principle is to eliminate human intervention wherever possible. Manual backups are prone to error—they get forgotten, misconfigured, or skipped. Automation is the cornerstone of a consistent and dependable backup process, ensuring that backups execute on schedule without fail.
For a deeper dive, check out our guide on the benefits of automated daily backups for your business.
Verifying Your Backups with Test Restores
A "backup successful" notification merely confirms that a file was written to disk. It provides no guarantee of that file's integrity or its viability for a full recovery. The only way to truly validate a backup is to perform regular, documented test restores.
This procedure involves restoring a recent backup to an isolated staging environment—a sandboxed replica of your live site. This allows for thorough validation without impacting your production website. For example, creating a subdomain like staging.yourwebsite.com and restoring the latest backup there.
What to Check During a Test Restore:
- Data Integrity: Verify file checksums and run database integrity checks (e.g.,
CHECK TABLEin MySQL) to ensure no corruption occurred. - Functionality: Execute a test transaction. Can a user create an account? Can they add an item to the cart and complete the checkout process?
- Completeness: Confirm that all assets, including recently uploaded images, theme customizations, and plugin settings, were restored correctly.
Regular testing and proactive health checks are critical, just like effective preventive and corrective maintenance are for any business asset. Schedule and perform a full test restore on a quarterly basis, at minimum, and after any significant architectural changes to your site.
Defending Against Modern Ransomware Threats
Modern cyber threats have evolved to specifically target backup repositories. Advanced ransomware strains are designed to first find and encrypt or delete your backups before attacking your live systems, thereby eliminating your ability to recover.
The statistics are alarming. According to recent cybersecurity reports, ransomware now directly targets backup systems in up to 94% of attacks. With the average cost of a data breach in the U.S. hitting $10.22 million, a ransomware-resilient backup strategy is an absolute necessity.
An immutable backup is one that cannot be altered, encrypted, or deleted by anyone—not even an administrator with full credentials—for a set period. This makes it your ultimate defense against ransomware.
To counter these threats, your strategy must incorporate advanced defensive layers:
- Immutability: Utilize cloud storage services that support "Object Lock" or "WORM" (Write Once, Read Many) features. For example, configuring an AWS S3 bucket with Object Lock in compliance mode makes the backup data unchangeable for a defined retention period, rendering it impervious to ransomware encryption.
- Air-Gapped Storage: This refers to storing a backup copy completely disconnected from the network. While traditionally done with physical tapes, a modern equivalent is using a cloud storage account with separate, unique credentials that are not used for any other system and are stored securely offline.
By automating your process and consistently verifying its integrity, you build a recovery plan that isn't just reliable—it's truly resilient against the worst-case scenarios.
FAQs: Expert Answers to Common Backup Questions
Navigating the specifics of a backup strategy often leads to practical questions. Here are expert answers to the most common queries we receive from business owners.
How Often Should I Actually Back Up My Site?
This is determined by your Recovery Point Objective (RPO). The correct question is not "How often should I back up?" but "How much data can my business afford to lose?"
- Example 1 (Low Change Rate): A corporate blog updated twice a month has a high tolerance for data loss. A weekly backup (RPO of 7 days) is perfectly adequate.
- Example 2 (High Change Rate): An active e-commerce site processing orders continuously cannot afford to lose hours of data. The backup frequency must match the RPO. If the RPO is 15 minutes, you need a mechanism (like transaction log shipping or frequent incremental backups) that runs every 15 minutes.
Your backup frequency must always be greater than or equal to your RPO requirements.
Can I Just Use My Web Host's Backups?
Relying solely on your hosting provider's backups is a significant strategic risk. These backups are typically designed for the host's internal, server-wide disaster recovery, not for granular, customer-initiated restores.
Key limitations include:
- Lack of Control: You often cannot control the backup schedule, retention policy, or storage location.
- Slow Recovery: Restoring from a host-level backup can be a slow process that requires filing a support ticket and waiting for an administrator, which may not align with your RTO.
- Single Point of Failure: If the hosting company itself has a major outage or security breach, both your live site and your backups could be compromised simultaneously.
A host backup should be considered a tertiary, last-resort option. Your primary, independent backup strategy puts you in full control of your data's destiny.
What’s This 3-2-1 Backup Rule I Keep Hearing About?
The 3-2-1 rule is a time-tested, industry-standard best practice for ensuring data resiliency. It's a simple, vendor-agnostic framework that protects against nearly any failure scenario, from single-file corruption to a regional disaster.
Here’s a practical application:
- THREE Copies:
- Your live production data.
- A primary backup copy.
- A secondary backup copy.
- TWO Media: Store the copies on at least two different storage types. For example, the primary backup goes to a local NAS device (spinning disk), while the secondary copy goes to cloud object storage (e.g., Amazon S3). This protects against failures specific to one type of hardware.
- ONE Offsite: At least one of the backup copies must be stored in a separate physical location. Replicating your backup to the cloud inherently satisfies this requirement.
Implementing the 3-2-1 rule is one of the most effective measures you can take to guarantee the recoverability of your business data.
A great website is built on a foundation of security and reliability. At Websites USA, we design, build, and maintain websites with bulletproof, automated backup strategies that let you sleep at night. Let us handle the technical side so you can focus on what you do best. Learn more about our comprehensive website services.


